Organisations across the region face a regulatory environment that has changed dramatically over the past twenty-four months. The theme for this year’s international observance, “Take control of your data,” resonates particularly strongly in a region where comprehensive data protection laws have proliferated, enforcement mechanisms have matured, and artificial intelligence has simultaneously created both unprecedented opportunities and novel risks.
A region transformed by regulation
The regulatory architecture governing data in Southeast Asia has fundamentally shifted. Vietnam’s Law on Personal Data Protection, passed in June 2025 and effective from 1 January 2026, represents the most significant recent development.
The law establishes personal data protection as an independent legal right and introduces penalties of up to 3 billion VND for administrative violations, with fines for illegal data trading reaching ten times the revenue obtained from the violation.
The enforcement context is sobering: Vietnamese authorities detected 56 cases involving over 110 million illegally traded data records in the first half of 2025 alone.
Indonesia’s Personal Data Protection Law has been fully enforceable since October 2024, though implementing regulations are still being developed. The absence of a dedicated supervisory authority has created uncertainty for organisations seeking to operationalise cross-border transfer provisions.
Meanwhile, Malaysia’s phased implementation of its Personal Data Protection (Amendment) Act 2024 concluded in June 2025, introducing mandatory data breach notification, data protection officer requirements, and a substantial increase in penalties to MYR 1 million.
A draft amendment introduced in mid-2026 proposes restructuring lawful bases for processing to align with the GDPR, repositioning consent as one of seven coequal bases rather than the default requirement.
Across the region, the intersection of artificial intelligence and data privacy has emerged as the defining challenge for 2026. TrustArc’s 2026 Global Privacy Benchmarks Report reveals that 69% of professionals now use AI tools frequently at work, while 24% report problems arising from AI-driven decisions — an increase of seven percentage points from the previous year.
The report identifies a widening “capability gap”: organisations with integrated privacy initiatives achieve competence scores nearly four times higher than those with fragmented, manual processes.
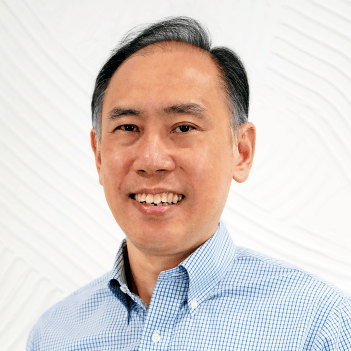
This finding aligns closely with the perspective offered by Wee Tee Hsien, chief executive officer of FUJIFILM Business Innovation Singapore, who argues that organisations must “shift their mindset from compliance to stewardship.”
Wee Tee Hsien
“Privacy should be embedded by design, not retrofitted after deployment,” and that disciplined data governance requires clarity on “how data can be reused, retained, or used for model training”. Wee Tee Hsien
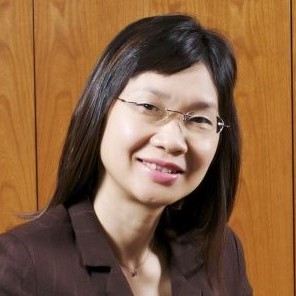
Rachel Ler, area vice president of Asia at Fastly, underscores the enduring fundamentals in this AI-driven context: “accountability and transparency are paramount.” She stresses that “organisations are still responsible for how data is collected, processed, and protected, whether AI systems, cloud platforms, or channel partners handle it”.
Ler also highlights the importance of ensuring that “employees who handle personally identifiable information understand what can and cannot be shared with AI tools,” requiring “clear, enforceable AI policies that define approved use cases and explicitly prohibit the use of customer or sensitive data when interacting with AI models”.
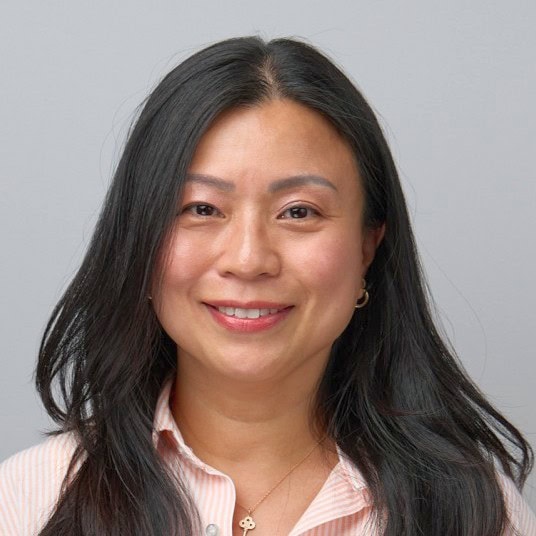
Lim Hsin Yin, vice president of Sales for ASEAN at Cohesity, frames the challenge in terms of control and accountability: “AI delivers powerful insights, but it can also amplify risk if data is not properly governed.”
Lim Hsin Yin
She argues that “organisations must ensure AI systems only access data they can classify, secure, and recover — even during a cyber incident”. Lim further observes that “privacy is no longer solely an IT issue — it requires coordination across leadership, operations, and legal teams,” and recommends deploying robust data classification tools as a critical first step.
Cross-border complexity and regional interoperability
The ASEAN region’s diversity in data sovereignty and regulatory requirements complicates cross-border data flows. The Future of Privacy Forum’s July 2026 issue brief notes that while jurisdictions are increasingly converging around safeguards-based mechanisms, significant variations remain in approaches to cross-border transfers.
Data localisation measures have increased substantially across ASEAN, rising from just two in 2012 to twelve in 2023, with ten reflecting the most restrictive category requiring both local storage and prohibiting cross-border transfers.
Regional interoperability efforts continue to mature. The ASEAN Model Contractual Clauses, endorsed in 2021, provide a voluntary framework for compliant cross-border transfers, and Malaysia has explicitly recognised them as an adequate safeguard.
Negotiations on the ASEAN Digital Economy Framework Agreement, which will address cross-border data flows, represent a significant regional initiative to balance economic integration with privacy protection.
Accountability as the foundation
The common thread across regulatory developments, industry perspectives, and third-party research is accountability. Wee captures this with characteristic clarity: “Accountability must sit firmly with senior leadership.”
He calls for management to “actively oversee AI and data privacy risks, with clear ownership, metrics, and escalation mechanisms,” and notes that “AI systems evolve, so privacy risk must be continuously monitored through audits, testing, and independent assessments”.
Lim reinforces this resilience-oriented approach, arguing that “strengthening data privacy today also demands a shift from static controls to continuous cyber resilience”. She emphasises the importance of “adaptive architectures that monitor data across systems, applications, and infrastructure, with the ability to recover rapidly if compromised”.
Ler concludes with a perspective that resonates across the region:
Rachel Ler
“Privacy by design should therefore be embedded into AI strategies from the outset. This includes limiting data collection, improving visibility across hybrid and multi-cloud environments, and enforcing consistent security controls”. Rachel Ler
The imperative into 2027
As Southeast Asian organisations navigate the complex terrain of 2027, the imperative is clear. Regulatory frameworks have matured, enforcement has intensified, and the AI transformation has raised the stakes for responsible data stewardship.
The organisations that thrive will move beyond reactive compliance to proactive, accountable governance—embedding privacy into the fabric of their operations, investing in workforce capability, and treating data protection not as a constraint on innovation but as its essential foundation.